product
- What you can do with CrowdStrike
- CrowdStrike Modules Falcon
- Falcon Prevent(NGAV)
- Falcon Insight(EDR)
- Falcon OverWatch (Threat Hunting)
- Falcon Discover (IT Asset Management)
- Falcon Spotlight (vulnerability management)
- Falcon Adversary Intelligence
- Falcon Identity Threat Protection/Detection
- Falcon Cloud Security(CNAPP)
- Falcon Surface(EASM)
- Falcon Shield(SSPM)
- Falcon Next-Gen SIEM
service
Application for evaluation machine
- FAQ
CrowdStrike
Staying ahead of global threats
Next-generation security platform
CrowdStrike
CrowdStrike
マクニカは、13年以上の取り扱い歴と約1,500社の導入実績を持つ
CrowdStrikeの
ディストリビューター(一次代理店)です。
What is CrowdStrike?
Covering all attack domains with a single platform.
CrowdStrike is a cybersecurity platform that provides integrated protection across a wide range of security areas, including endpoint, identity, cloud, SIEM, and AI security.
Because it can be operated with a single agent and a single console, it streamlines increasingly complex security measures while flexibly expanding the necessary security functions to match evolving risks and business growth.
Integrating a wide range of functions into one.
NGAV、EDR、脆弱性管理、クラウド保護、ID保護、SIEM、AI保護など、幅広い機能を1エージェント・1コンソールで利用可能です。
Leveraging global threat intelligence to respond to unknown attacks
We aggregate event and threat intelligence collected from around the world and use it for detection that takes into account the latest attack methods.
Implementation with minimal impact on business operations
No on-premises management server is required. No reboot is needed during installation, and it supports Windows/Mac/Linux, etc.
Speeding up detection, investigation, and response.
We consolidate information in the cloud to support actions such as confirming detection details, investigating the scope of impact, and isolating devices.
We can solve these problems with CrowdStrike.
From ransomware protection to identity protection, cloud services, and operational efficiency, we'll introduce some typical challenges and how CrowdStrike Falcon can solve them.
We want to protect against external threats and ransomware.
- Targeted regional detection, protecting against known and unknown malware and fileless attacks.
- In the unlikely event of an intrusion, we will respond quickly with detection, investigation, and terminal isolation.
- Experts proactively detect advanced threats and reduce missed opportunities.
We want to be prepared for attacks that exploit IDs and authentication.
- Unauthorized access using legitimate IDs and abnormal authentication behavior are detected.
- Preventing damage through policy-based authentication blocking and MFA enforcement.
- Visualize and manage vulnerable AD configurations, privileged accounts, and SaaS configuration flaws.
We want to address the risks associated with using the cloud.
- Visualize assets across multiple clouds and detect misconfigurations and threats.
- Protect cloud workloads and prevent data breaches.
- Centralized auditing of SaaS configurations ensures secure usage.
We want to streamline and improve our operations.
- By consolidating a wide range of functions into a single console, the operational burden is reduced.
- Detect and investigate logs, including those from CrowdStrike and other sources, on a single screen.
- Managed operations by experts compensate for the lack of personnel and organizational structure.
We want to manage the risks associated with using generative AI.
- Visualize the use of generative AI within the organization and strengthen governance.
- Control the input of confidential data and PII to prevent information leaks.
- Enabling the application of AI usage policies and risk detection.
I want to understand and manage vulnerabilities and attack surface areas.
- Real-time visualization of terminal and server vulnerabilities and patch application status.
- Identify publicly disclosed assets and clarify the risks that need to be addressed.
- Prioritize based on risk and streamline response.
CrowdStrike Feature List
Endpoint security
Identity Security
cloud security
Integrated log management and analysis
Exposure Management
AI and Data Security
Operational support/advancement
Others
Reasons for adopting CrowdStrike from Macnica
マクニカは、13年以上・1,500社以上の導入実績をもつCrowdStrikeのディストリビューター(一次代理店)です。
Extensive implementation track record and support system
CrowdStrike products
Number of companies that have implemented the system
1,500+companies
Customers in a wide range of industries
We have implemented it for you.
Handling history
13 years
2013年 CrowdStrike
日本法人設立前より
ディストリビューターとして
取り扱いを開始しています。
CS-related members
100 people+
Presales, Customer
Success, support, etc.
CrowdStrike related
This is the total number of members.
Number of certified people
56 people+
- CCCS2 people
- CCFA30 people
- CCFH2 people
- CCFR13 people
- CCIS3 people
- CCSE6 people
Number of support cases
12,500+
From our contracted users
This is the number of inquiries handled. (FY2025)
Based on our extensive product knowledge,
We provide support for operation and utilization after implementation.
Macnica Support Services
Macnica provides comprehensive services from implementation to utilization, including not only maintenance and support. We don't simply "install the product and forget about it"; a dedicated representative works alongside our customers to ensure their operational adoption and effective use.
introduction
Supporting a smooth launch
free trial
Before implementation, you can verify the agent load and detection performance in your own environment.
Easy consultation service during implementation
A dedicated representative will provide support through consultations for the first month after implementation. This will ensure a smooth implementation by running in parallel with standard support.
Implementation support (optional)
A dedicated representative will provide support for the first two months after implementation through operational training, QA support, and regular meetings.
operation
Supporting smooth and uninterrupted operations.
technical support
We provide support via email/web form during weekdays from 9 am to 5 pm. Technical QA and troubleshooting services are available in Japanese.
24365 support (optional)
We have expanded the scope and content of our incident response. We will now handle P1/P2 incidents from initial notification to complete recovery.
Extra support (optional)
In addition to email, we also accept inquiries by phone and web conference.
Health check service (optional)
We conduct regular reviews of the configuration status and provide the latest update information through meetings. We review the environment based on the differences from Macnica 's recommended settings to reduce operational workload and prevent omissions in support.
exercise
Supporting mastery of the technology and in-house development.
Assisted Pass (Optional)
Our engineers will assist with all tasks related to CrowdStrike infrastructure operations. With 40 tickets per year, we aim to create an environment where our clients can focus on their core business (planning, security operations, etc.).
Various training
We offer training tailored to your needs, including basic, advanced, CTF-style, and hands-on sessions using simulated attacks.
User Group Meeting / Technical Update Seminar
In addition to user meetings (Falcon Tech (CTF), module introduction seminars, etc.), we will also provide important updates in webinar format.
CrowdStrike user community "Falcomi"
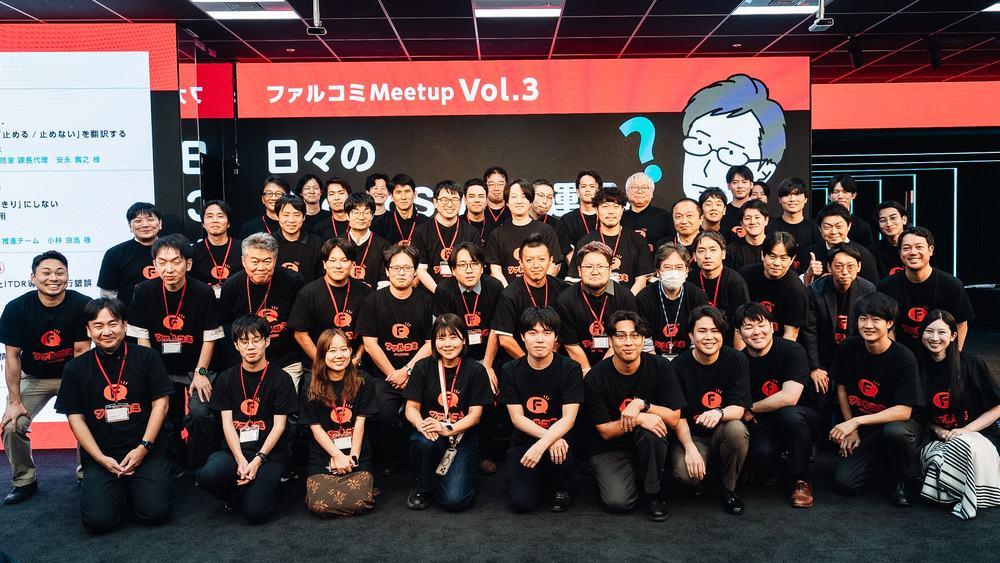
Falcomi, operated by Macnica, is a community for CrowdStrike users.
We provide a platform for users to share their operational knowledge, challenges, and lessons learned based on their experiences.
CrowdStrike user community "Falcomi"
-
Onboarding content during implementation
We offer a variety of content to help you get started with using the system smoothly.
-
Information exchange in online communities
We support your daily operations by providing information on CrowdStrike setup, operational tips, and technical updates through Q&A and knowledge sharing among users.
-
User-exclusive event
We regularly hold Meetup events and CTFs, providing opportunities for users to exchange information and stay up-to-date with the latest information.

Case study


Holdings


DeNA


Kagawa University


FAQ
Here are answers to frequently asked questions from our customers regarding the implementation and operation of CrowdStrike.
Q: Which operating systems are supported?
It supports multiple operating systems, including Windows, macOS, and Linux.
Q: Can I try it out before implementing it?
Yes. Macnica offers a free trial, allowing you to test the agent load and detection performance in your own environment. Click here for the free trial.
Q: Can it coexist with antivirus software from other companies?
Yes. While we do not recommend coexisting with conventional antivirus software, it is possible to coexist by performing the necessary settings (AV coexistence settings and mutual exclusion settings). Please contact us for details.
Q: Will the device detect malware even when it's offline?
Yes. While we do not recommend using the service offline at all times, detection and blocking will still occur in offline environments. Please note that some features that involve cloud queries will only be enabled when connected to the cloud.
Are all hosts on which the Q agent is installed covered by the license?
No. The license is calculated based on the average number of agents (Falcon sensors) that came online at least once during the most recent four-week period, divided into seven-day intervals. Please contact us for more details.
Q: How are licenses counted in VDI and SBC environments?
Generally, a license is required for each environment in which the OS runs. The specific method for counting licenses in VDI/SBC environments varies depending on the configuration, so please contact us for details.
Q: Is it possible to install and uninstall Falcon sensors even in an offline environment?
Yes, it is possible by following the prescribed procedure. Since uninstallation does not involve communication with the cloud, you can uninstall it as usual. Please contact us for details.
Q: When migrating from a verification license to a production license, is it necessary to reinstall or reconfigure the Falcon sensor?
No reinstallation or reconfiguration is required. You can migrate your test tenant directly to your production tenant. Please contact us for details.
Q: What are the advantages of implementing from Macnica?
マクニカは13年以上・約1,500社の導入実績を持つCrowdStrikeのディストリビューター(一次代理店)です。導入前の検証支援から、日本語による運用サポート、技術問い合わせ対応、ユーザーコミュニティ「ファルコミ」の提供まで、導入から運用定着までを一貫して支援できる点がメリットです。
Inquiry/Document request
In charge of Macnica CrowdStrike Co., Ltd.
- TEL:045-476-2010
- E-mail:crowdstrike_info@macnica.co.jp
Weekdays: 9:00-17:00