- CPS Security Business HOME
- Handling Manufacturer
-
Solution service

-
column·
example
- Document
-
Seminar
On-Demand Video
- Inquiry


Dragos
The world's highest peak
OT Security Using Threat Intelligence

Dragos is a company founded by OT security experts who have worked for U.S. government agencies and the military, analyzing and responding to national-level cyber threats targeting critical infrastructure.
Based on the philosophy that protecting the OT environment means protecting social infrastructure and people's lives, we incorporate the knowledge gained from responding to actual attacks and our unique threat intelligence into our products and services.
Currently, it is used by numerous companies in over 20 countries worldwide, primarily in critical infrastructure and manufacturing sectors, providing comprehensive OT security from OT asset management to threat detection and incident response.
We have been recognized as a Leader in the Magic Quadrant™ for CPS Protection Platforms.
Gartner®, Magic Quadrant™ for CPS Protection Platforms, Katell Thielemann et al., 12 February 2025
GARTNER is a trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and other countries, and MAGIC QUADRANT is a registered trademark of Gartner, Inc. and/or its affiliates and is used herein with permission. All rights reserved.
Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner's research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
Features of the Dragos Platform
| Cyber Hygiene Functions for prevention |
Cyber resilience Useful responses when a cyberattack occurs |
|||
| Assets, communications, Protocol visualization |
Vulnerability management | Collective Defense | Threat Detection | Incident response support |
| Asset visualization Identifying assets through traffic analysis and active discovery Communication and protocol visualization High identification capability using DPI method |
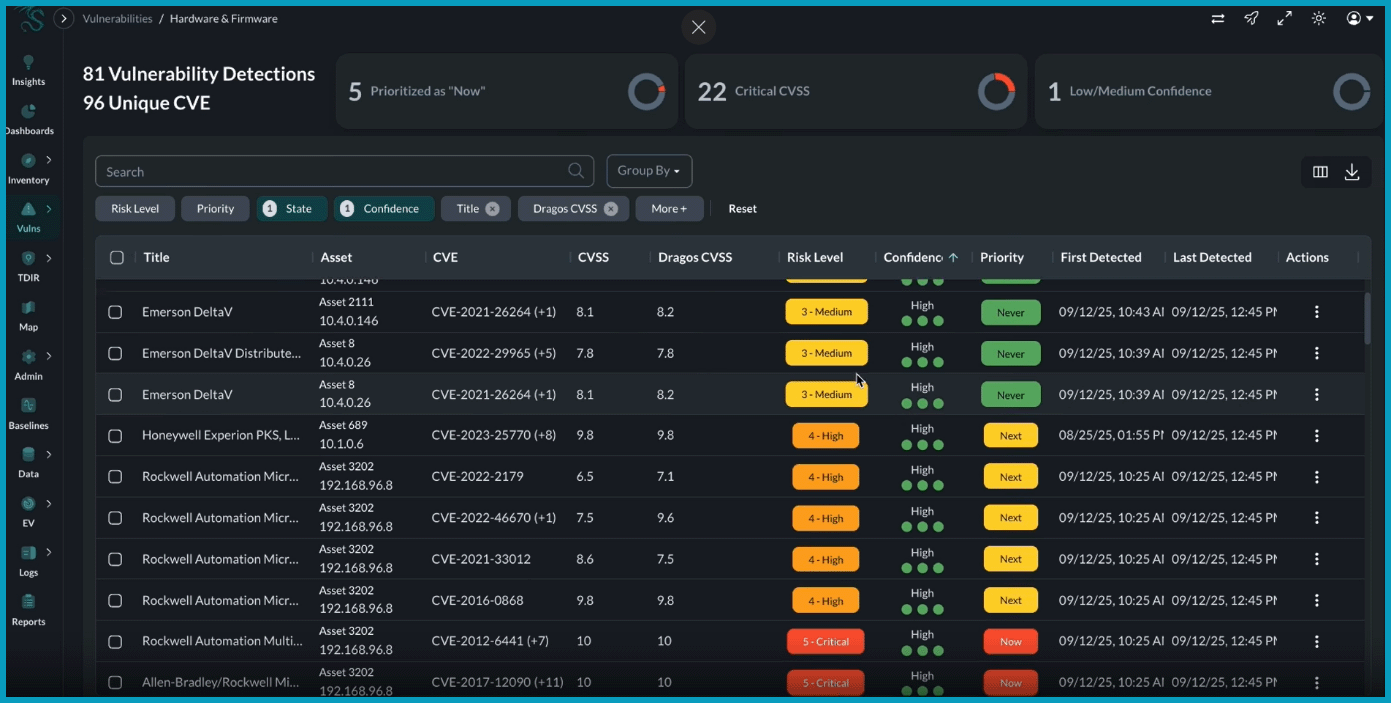
Vulnerability visualization Risk indication based on threat intelligence Prioritizing Now, Next, and Never, and presenting alternative mitigation measures. |
Collective Defense Anonymous sharing of customer detections |
Detection linked to attack scenarios Detection based on real cyberattacks by attack groups around the world High detection capability and attack identification capability Four detection models optimize detection results, enabling identification that is not overwhelmed by false positives. |
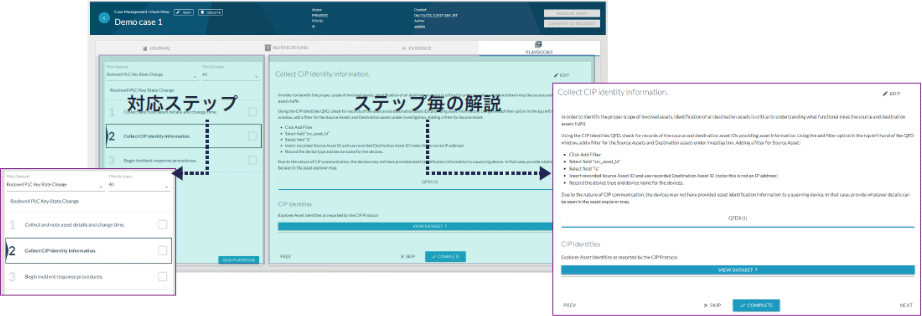
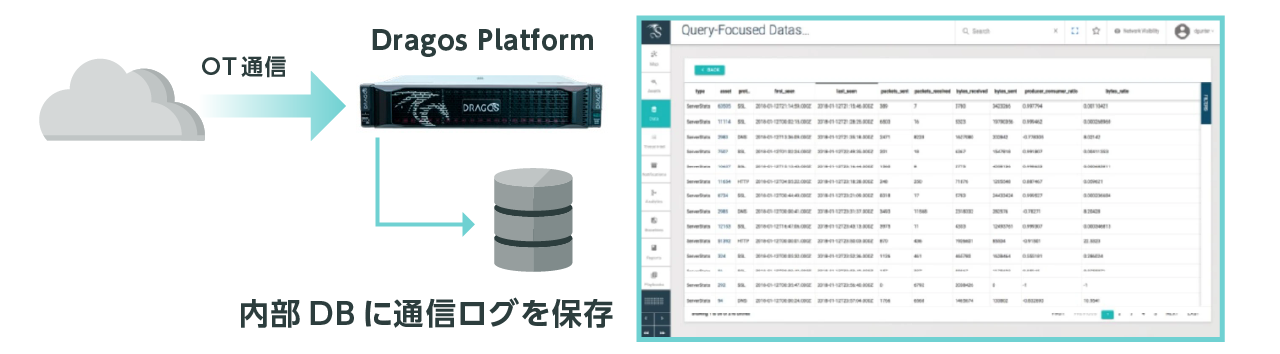
Playbook The procedure for handling the investigation is described in steps. Supporting initial response investigations QFD (Forensic Assistance Function) for infringement investigations It retains communication records, allowing for quick reference of communications between devices and IOCs (Indicators of Control). |
| We can also provide services such as platform operation and monitoring support upon request. | ||||
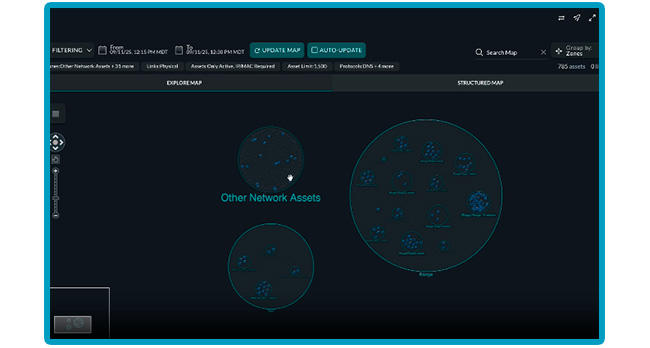
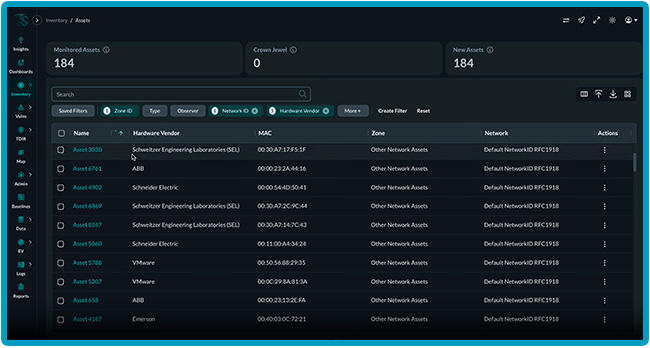
Feature 1: Flexible and wide-ranging OT monitoring technology
- Accurate asset identification and communication identification
- Understand the security baseline and topology.
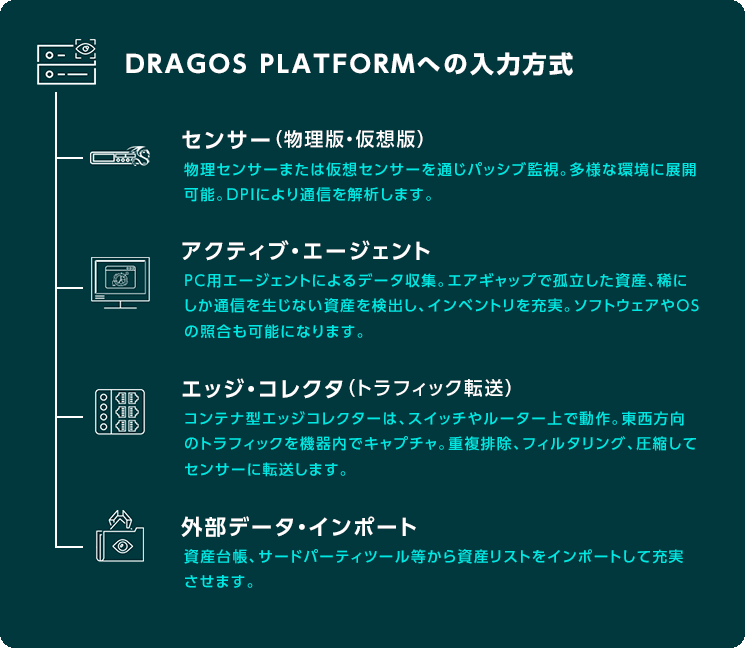
- Monitoring and operation can be performed passively, while technologies to enhance asset identification can be utilized (see diagram on the right).
Feature 2: Intelligence-driven threat detection
Achieve optimal monitoring and response tailored to your workflow.
DPI technology allows us to capture deep tissues.
- MODELING
- Flexible and precise baseline monitoring using DPI (manual and learning-based)
- CONFIGURATION
- Monitoring network and equipment configuration and status changes.
- THREAT BEHAVIOR
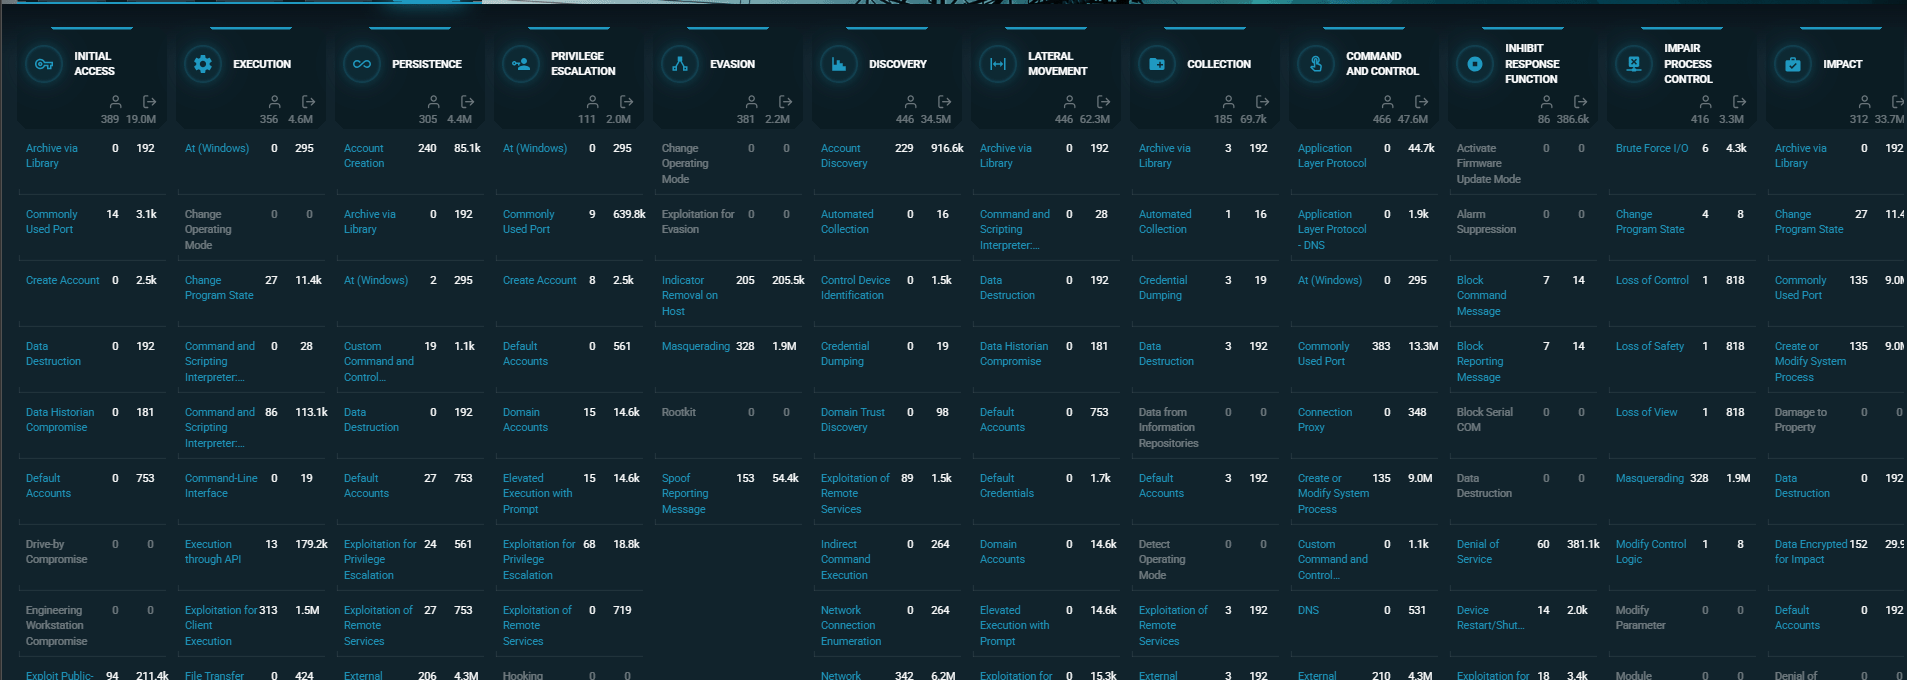
- Detecting attacker behavior (TTP)
- INDICATOR
- Indicators of a Critical Action (IOC) detected.
Equipped with Dragos' advanced OT cyber intelligence.
- Latest detection patterns/IOCs (Regularly updated + Unscheduled updates)
- The OT attack methods and countermeasures against attack groups are clearly defined.
- UI for rapid incident response and security analysis
- Threat Intelligence Report *option
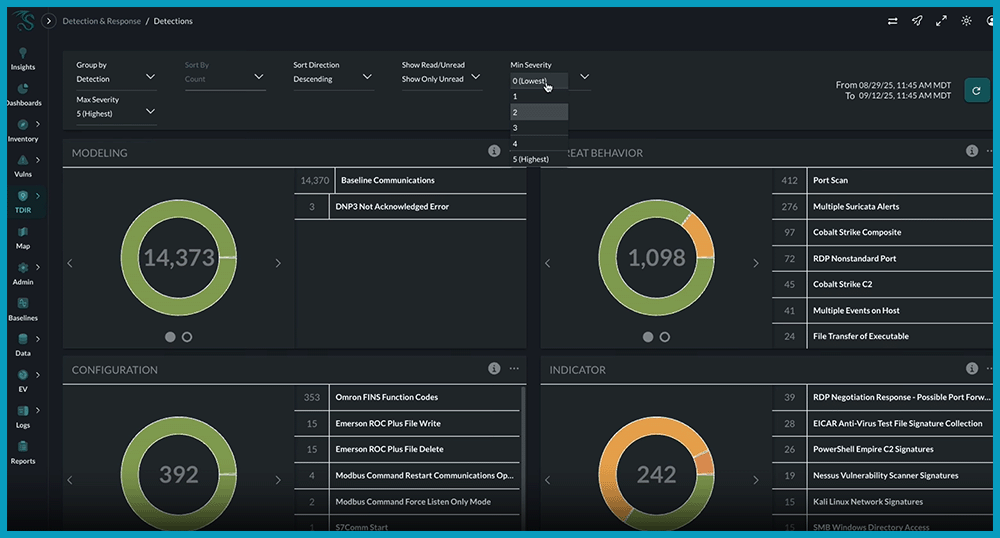
It is determined based on the degree of impact (Consequence) and the certainty of detection (Confidence).
Therefore, it is possible to distinguish between a cyberattack and an operational anomaly.
Severity 4: High-risk, suspicious behavior detected in the OT environment → Incident response
Severity 3: Detects significant environmental changes or activities → Threat hunting
Severity 2: Communication-related events that could potentially be used for attacks → No action required
Severity 1: Events used to understand the situation for analysis, such as communication behavior.
Severity 0: Events that serve as information sources to improve the analytical context.
Feature 3: Excellent detection, investigation, and incident response
Equipped with numerous playbooks created by Dragos experts, providing a comprehensive approach for conducting investigations and incident response within limited timeframes.
- Playbook for each detected event
- We will present the response steps and decision points.
- Explanation of normal operation and attack methods, and how to distinguish between normal and false positives.
- Information gathering and response methods
- Incident Response Service Call
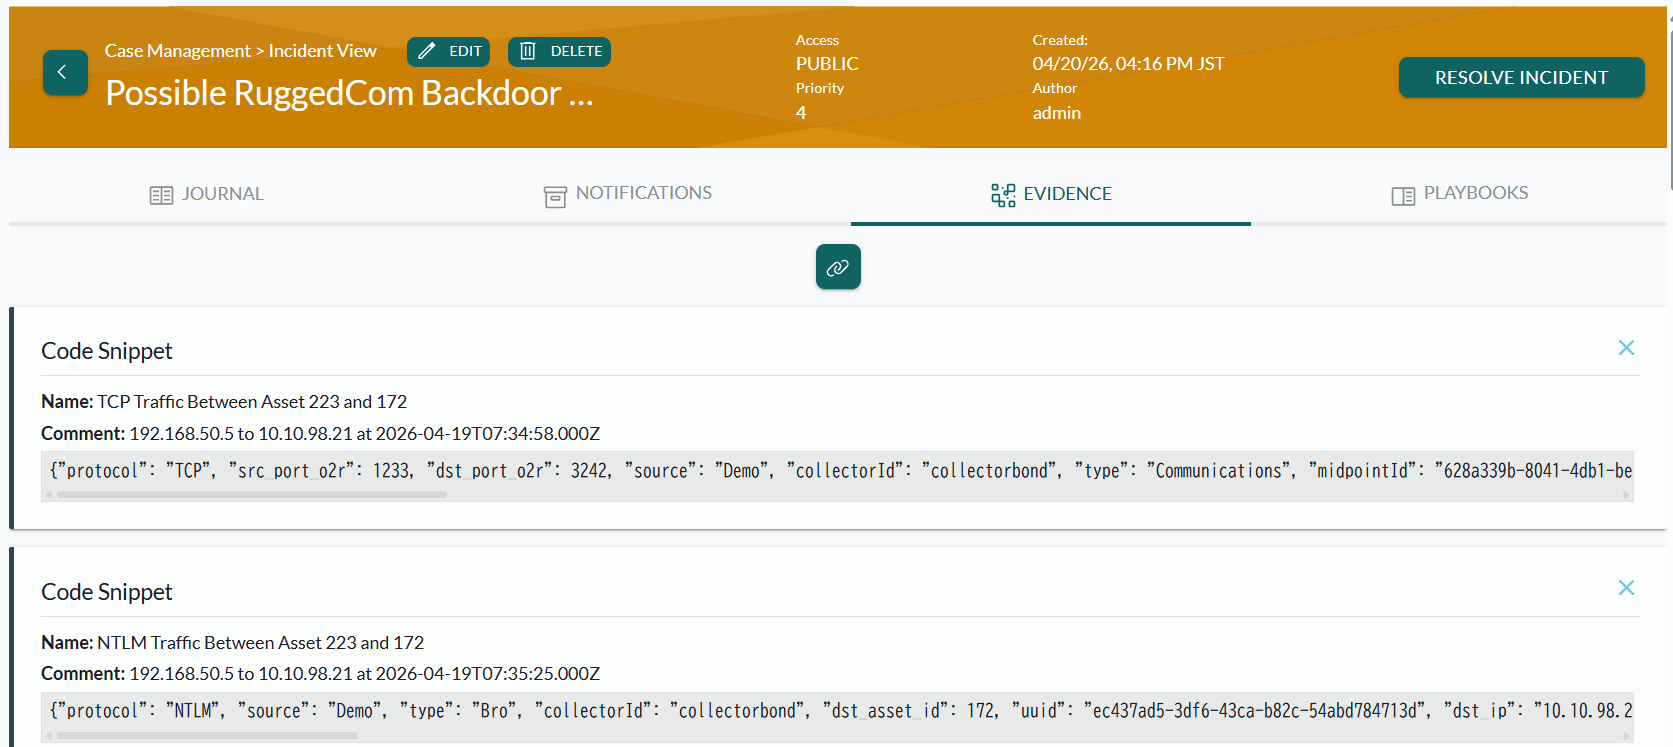
Centralized management of related activity logs, forensic data, samples, threat reports, timelines, and playbooks. Users can easily create cases and begin investigations.
Communication logs: Stored in the Dragos Platform internal database (for approximately 3 months).
Communication (Communication Analysis): A UI for analyzing assets and communications.
QFD, Kibana: Query Focused Dataset - Use Kibana to quickly search and investigate network behavior related to detection and indicators.
- Standard queries can be easily called from playbooks.
- You can also perform detailed manual searches and analyses.
Feature 4: Asset risk mitigation (vulnerability, end-of-life)
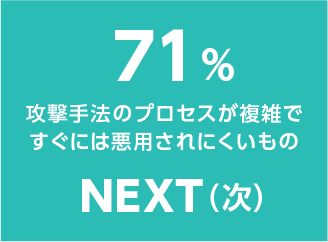
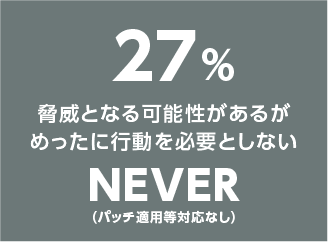
The NOW - NEXT - NEVER guidance allows you to focus on vulnerabilities that are exploited in cyberattacks. You can leverage limited team resources and reduce risk while minimizing downtime.
Dragos analysts analyze publicly available vulnerabilities in NVD. The vulnerabilities are scored, enriched, and prioritized based on their OT context, making them available for mitigation. Clear mitigation guidance enables vulnerability management across hardware, software, and operating systems.
We collect vendor EOS/EOL information. Lifecycle management enables risk reduction and mitigation planning.
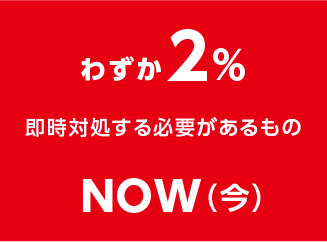
Focus resources on the most critical risks.
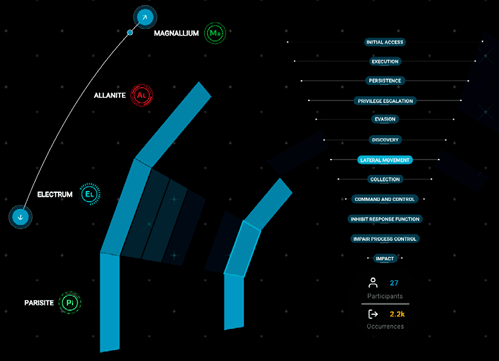
Feature 5: Community Defense
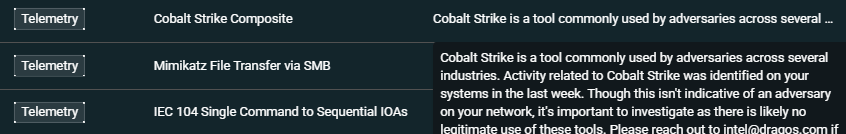
- Visualize the detection status (anonymized) of Dragos users worldwide. This enables proactive defense based on a grasp of the situation.
- Threat intelligence is automatically supplied to the Dragos Platform to respond to the latest threats.
* The threat intelligence included in the Dragos Platform is updated by applying the “Knowledge Pack.” Using NK will automatically acquire and apply it.
- Sharing and visualizing threat data
- Strengthening defenses
- Intelligence update
- Receive important security alerts
Feature 6: Enhanced research and analysis using AI
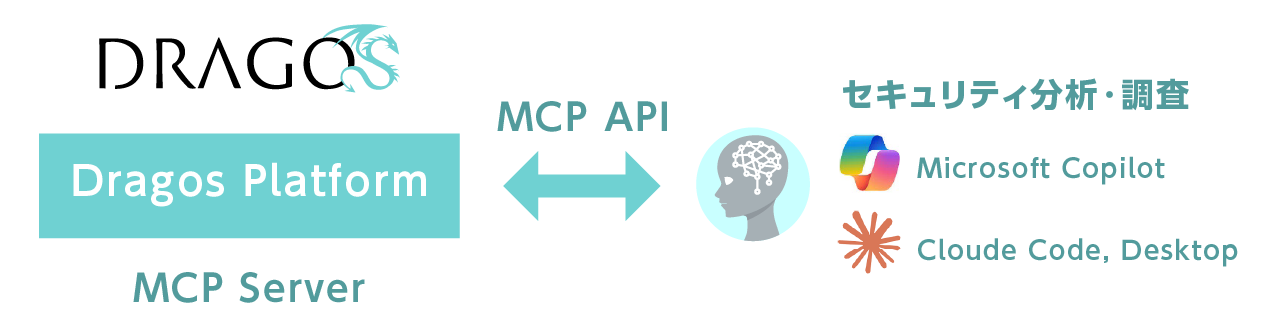
This is an interactive AI that combines the collection of detection data from the Dragos platform with the collection of OT cyber intelligence to assist in analysis.
We will strengthen our team of security analysts.
Leverage research from the world's largest OT threat intelligence team, WorldView reports, vulnerability analysis, and threat actor profiling. Directly integrate OT cyber expertise into analyst workflows.
MCP is LLM's native standard API interface, enabling integration with your existing generative AI.
The data detected by the Dragos platform (assets, vulnerabilities, communications, and various other detections) can be used by AI.
Available in both cloud and on-premise versions.
Typical Dragos Platform Deployment Configurations
Centralized monitoring of all factories (locations) nationwide from headquarters. This enables a comprehensive understanding of the company's security status and coordinated incident response in the event of an emergency.
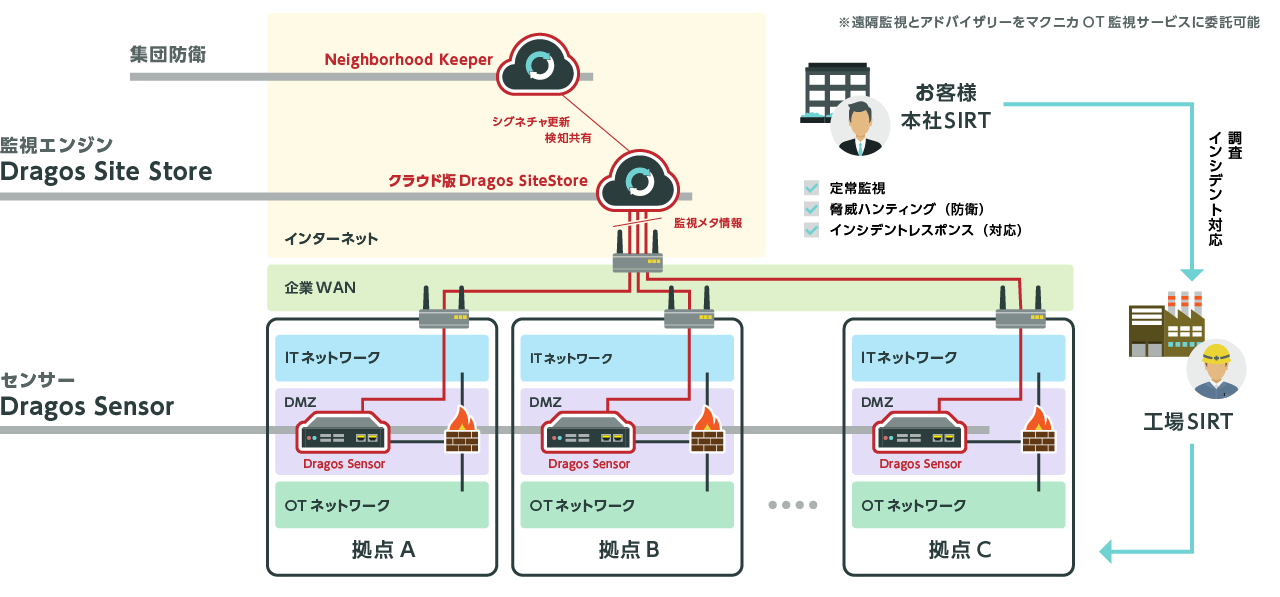
*This is a typical example where sensors are placed in the DMZ and the monitored traffic is on the OT network. This configuration has a proven track record in Japan.
We have experience with configurations where both SiteStore and Sensor are deployed in the OT environment, as well as configurations where they are installed on the IT side and mirror the monitored OT network.
company description
| company name | Dragos |
|---|---|
| Established | 2016 |
| location | Hanover, Maryland, USA |
| representative | Robert M. Lee |
| website | https://www.dragos.com/ |
Dragos
Robert M. Lee
Co-founder and CEO Rob Lee is a leading expert in OT/ICS security, with experience in critical infrastructure defense within the U.S. Air Force. Having been involved in the analysis and response to attacks such as the Ukrainian power grid attack and the TRISIS attack, he advocates threat-driven OT security measures based on the idea that "protecting OT means protecting social infrastructure and human lives."
Inquiry/Document request
In charge of Macnica Dragos Co., Ltd.
- TEL:045-476-2010
- E-mail:dragos-sales@macnica.co.jp
Weekdays: 9:00-17:00