Okta
Octa
What is SAML?
1. What is SAML? — Understanding the Basics
When working in a company, you use many cloud services every day. Managing separate IDs and passwords for each service is difficult, so many companies have employees log in to an authentication service (IdP) like Okta first, and then access each service from there. SAML (Security Assertion Markup Language) is one of the common rules (protocols) that make this "bulk login" possible. This article will explain it using Okta, a representative authentication service, as an example.
[SSO is not equivalent to SAML]
SSO and identity federation are the "desired outcomes (goals)," and SAML is one of the "means" to achieve them. The same objectives can also be achieved with OIDC (OpenID Connect) and WS-Federation (we will compare them in Chapter 5).
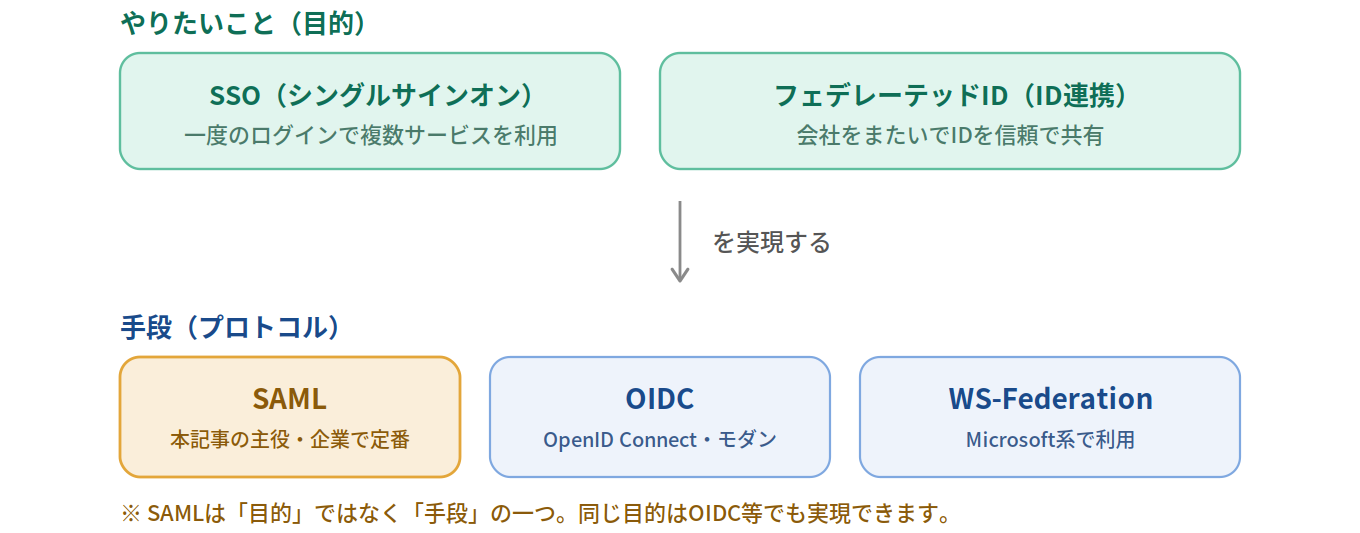
Figure: Relationship between SSO and SAML (Purpose and Means)
SAML is a standard developed by OASIS, and the version currently in widespread use is 2.0 (SAML 2.0). Authentication information is described in XML (a format of character data where the structure is represented by tags).
Two uses that SAML enables
- Single Sign-On (SSO)
With a single authentication, you can continue using multiple services without having to log in again. For example, once you log in to Okta, you can use Slack and Salesforce without having to log in again. - Federated Identity / ID Linking
This system allows IDs to be shared across companies based on "trust." Users managed and authenticated by another organization can be seamlessly accepted into your own organization's services.
There are three characters.
SAML communication involves the following three parties:
- IdP — Identity Provider
This is the party that verifies the identity of a person, guarantees that "this person is genuine," and issues a certificate (assertion). Examples: Okta, Microsoft Entra ID. - SP — Service Provider
This is the service provider's perspective. Users don't perform identity verification themselves; they trust the IdP's (Identity Provider) guarantees and grant access. Examples: Slack, Salesforce. - User (Browser)
This is the user. The SP and IdP do not communicate directly; they always communicate through this user's browser.
SAML assertion (proof issued by the IdP)
Once the Identity Provider (IdP) has completed identity verification, it issues a certificate stating, "This person is indeed genuine and is this kind of person." This is a SAML assertion. The Service Provider (SP) verifies this assertion and grants the user access. To prevent tampering, the assertion is digitally signed by the IdP.
Image of characters and their relationship of trust
The relationship between the three parties up to this point can be summarized in the following diagram. The SP and IdP have already established a trust relationship (exchange of certificates and metadata), and the user's browser carries the assertion during the actual login. Terminology (AuthnRequest, ACS URL, etc.) will be explained as it appears in the flow in the next chapter.
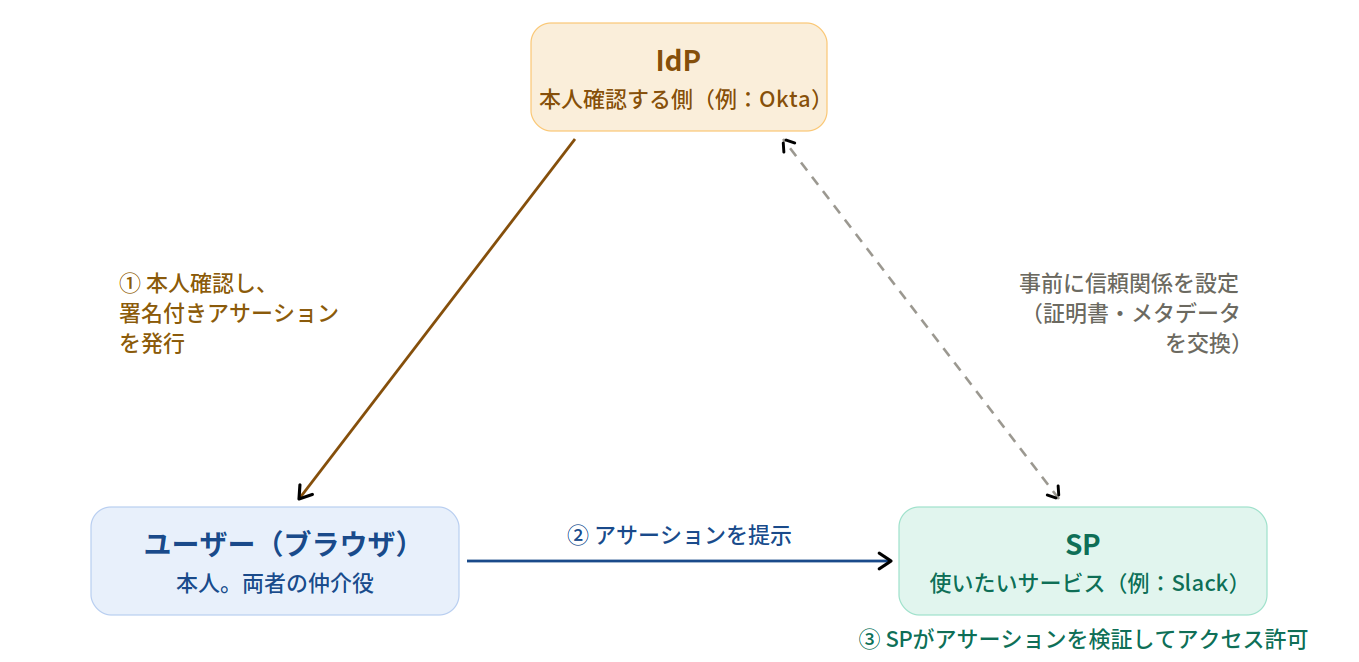
Figure: SAML Participants and Trust Relationships
2. Authentication process and Okta's role
Now, let's look at the actual order in which the login process proceeds. First, let me state just one premise.
[Premise: SP and IdP do not speak directly to each other]
SPs and IdPs do not communicate directly; all messages are delivered via redirection (automatic forwarding) in the user's browser. This is an important design feature of SAML, enabling them to cooperate even when they are not connected to each other on a network.
There are two types of flows, depending on which side they start from.
① SP-initiated
This pattern begins with the user attempting to open the app, and it accounts for the majority of SSO implementations in businesses. For example, if you open Salesforce from a browser bookmark, you are redirected to the Okta login screen, authenticated, and then returned to Salesforce.
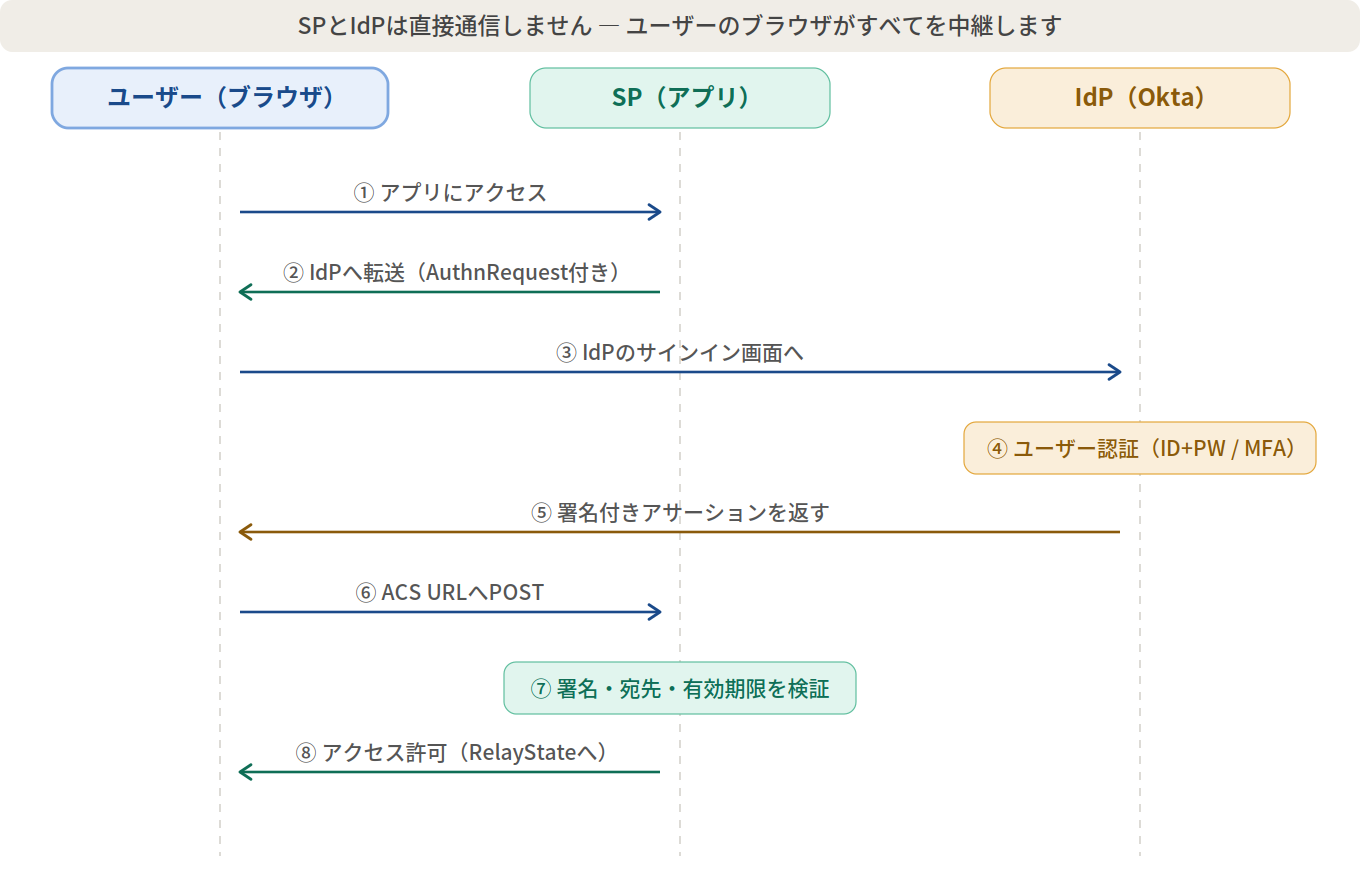
Figure: SP-initiated sign-in flow
The numbers in the figures correspond to the numbers in the text (① to ⑧).
- Access the app
The user opens a protected page. The app (SP) determines that the user is "not yet logged in." - Redirect to IdP (with AuthnRequest)
The app creates an AuthnRequest (verification request) and instructs the browser to forward to Okta (IdP). - Redirected to the IdP sign-in page
Your browser will redirect to the Okta (IdP) SSO URL, and the login screen will be displayed. - User authentication (ID + PW / MFA)
Users enter their ID and password in Okta and perform MFA (multi-factor authentication). - SAML Assertion (Signed XML)
If identity verification is successful, Okta creates an assertion, signs it, and returns it to the browser. - POST the assertion to the ACS URL.
The browser sends the assertion to the app's ACS URL (the URL where assertions are received). The app does not receive it directly. - Signature verification, user information retrieval, session establishment.
The application verifies the signature using the IdP's public key (X.509 certificate), confirms the recipient and expiration date, and then creates a session. - Accessing the app to grant permission (transition to RelayState)
This completes the login process. You will now be redirected to the "original page you wanted to open" as recorded in RelayState.
② IdP-initiated
This pattern begins with the user opening the Okta dashboard first and then clicking on the app icon listed there. The numbers (① to ⑤) in the diagram and text correspond to this pattern as well.
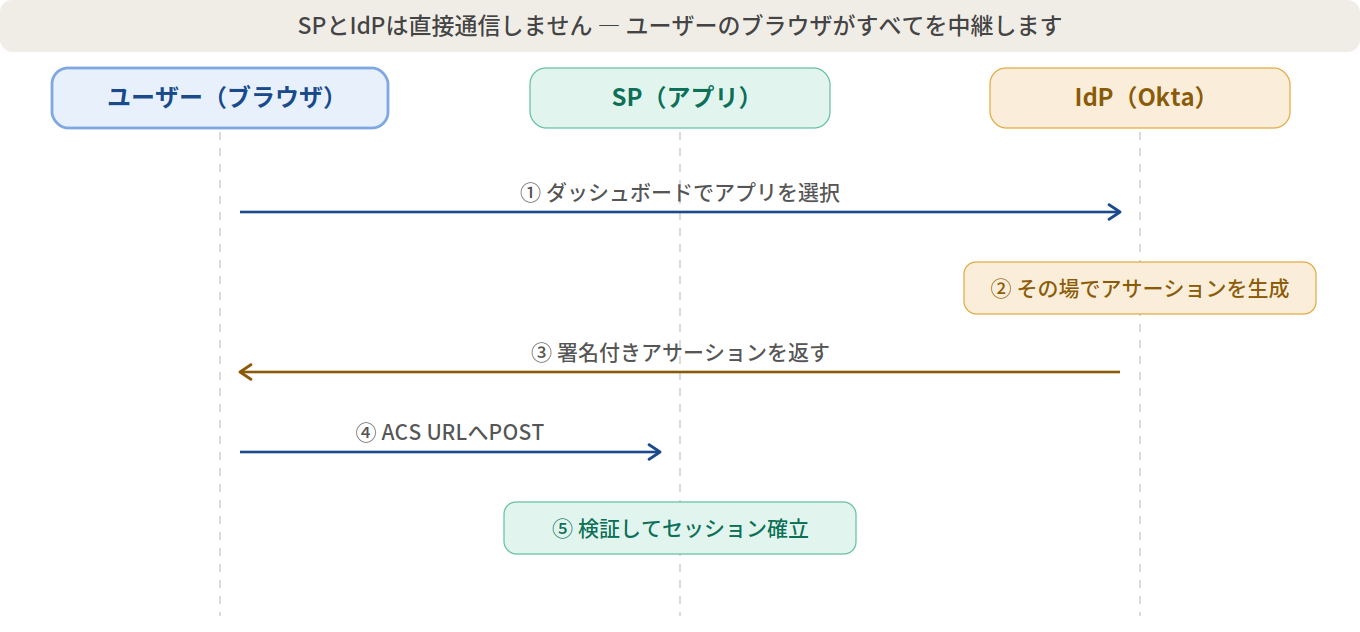
Figure: IdP-initiated sign-in flow
- Click the app on the IdP dashboard.
The user selects the icon of the app they want to use from the Okta dashboard. - Instantly generate SAML assertions
Okta creates assertions on the spot without waiting for an AuthnRequest (request for verification). - Return the assertion to the browser.
Okta passes the signed assertion to the browser. - POST to ACS URL
The browser sends the assertion to the app's ACS URL. - Verification and session establishment → Proceed to landing page
The app validates the assertion, creates a session, and displays a default page (landing page).
Okta can be both an IdP and a SP.
Up to this point, we've described Okta as an "IdP" (Independent Provider), but Okta can function as both an IdP and a Service Provider (SP) depending on the situation.
- If Okta is the Identity Provider (IdP): Okta manages the IDs and provides SSO to the Service Provider (SP). This corresponds to the "IdP = Okta" configuration in the flow described above.
- If Okta is the Service Provider (SP): When a company already has another Identity Provider (IdP), Okta itself trusts the authentication of the external IdP. Users authenticated by the external IdP are accepted into Okta using JIT provisioning (a mechanism that automatically creates Okta users upon initial sign-in).
→ Okta documentation: SAML app integration
3. Key points when configuring in Okta
First, as a prerequisite, there are two main ways to integrate an app with Okta. Many major SaaS applications, such as Salesforce and Slack, are registered in the OIN (Okta Integration Network) catalog as integrations validated and published by Okta, and most of the SAML configuration is already prepared simply by adding them from "Browse App Catalog" in the admin console.
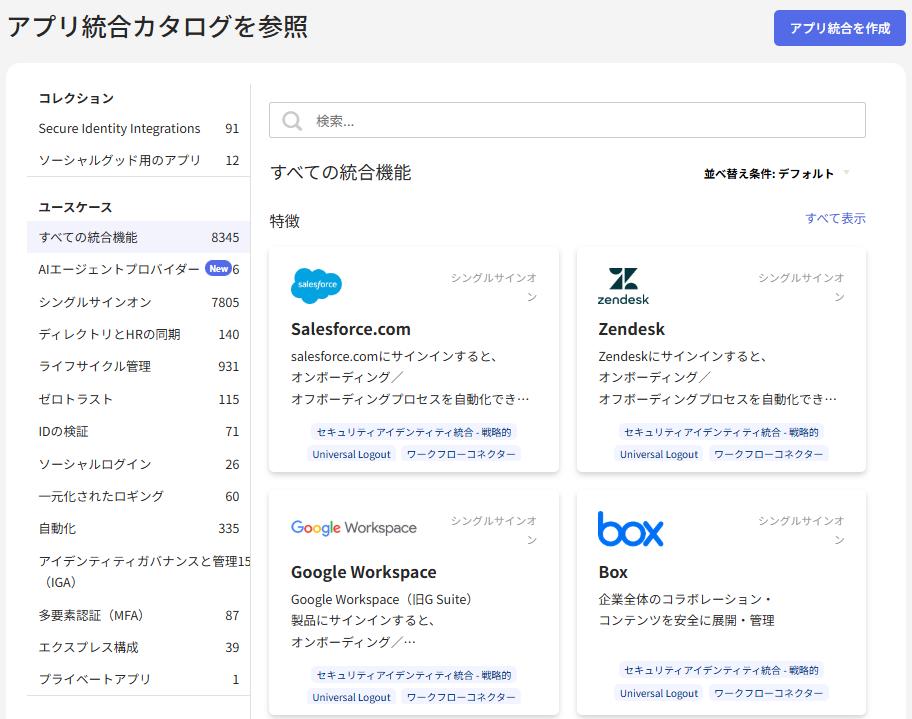
Figure: App Integration Catalog
For apps not listed in the catalog or proprietary apps, you will need to create them from scratch using the App Integration Wizard (AIW) ("Create App Integration" → "SAML 2.0").
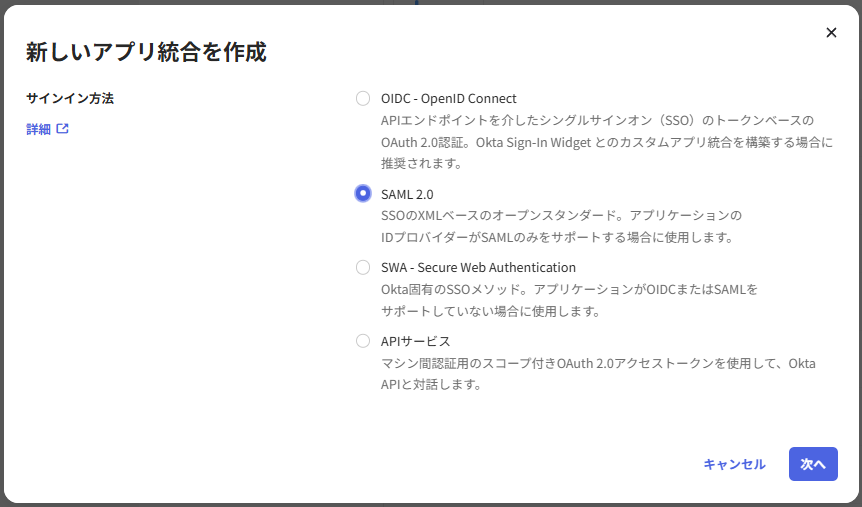
Figure: Creating an app integration
→ Okta documentation: Create an app integration
Below, we will summarize the items to consider when setting up AIW from scratch.
→ Okta Documentation: Reference for SAML Fields in the App Integration Wizard (Details of Each Setting Item)
Basic settings (required)
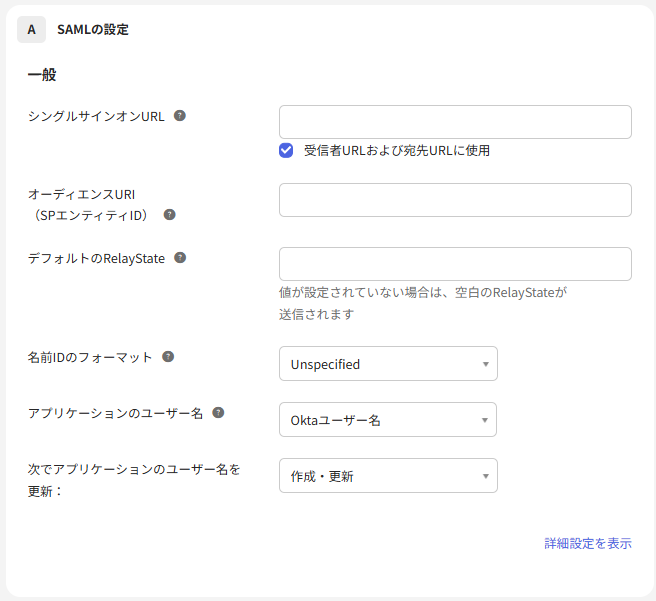
Figure: SAML settings (basic settings)
| Setting items | Contents/Notes |
| Single sign-on URL (=ACS URL) | This is the destination to which Okta posts assertions. It is also always used as the default destination for IdP-initiated sign-ins. Obtain this information from the service provider (SP) and enter it accurately. |
| Audience URI (SP Entity ID) | The identifier of the SP to which the assertion is directed. To prevent spoofing, it must strictly match the Entity ID on the SP side. |
| Default RelayState | This setting is used to return to a specific page after logging in (deep linking supported). In most cases, you can leave this field blank. |
| Name ID format | The format of the user identifier sent in the assertion (e.g., emailAddress). Okta's default is Unspecified. If no SP is specified, the default is fine. |
| Application username | The actual value sent as each user's app username (e.g., email address). Avoid using editable fields as this reduces security. |
Advanced settings
Opening "Show advanced settings" will reveal important security-related items. The main ones are as follows:
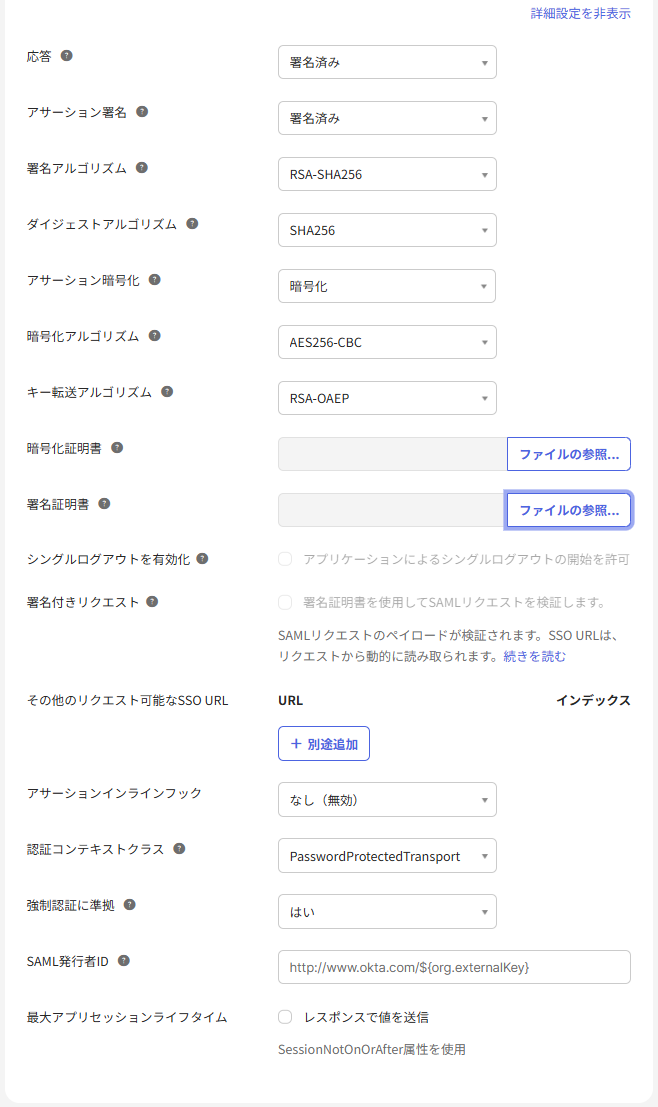
Figure: SAML settings (advanced settings)
| Setting items | Contents/Notes |
| Response/Assertion Signature | This specifies whether to sign the responses and assertions returned by Okta. Since signing is essential for tamper detection, it should be enabled as a general rule. |
| Signature algorithm / Digest algorithm | This is the algorithm used for signing. Okta's default is SHA-256. You can leave it as the default unless there are SP requirements. |
| Assertion encryption / encryption certificate | Should the assertion content be encrypted? Consider this if it contains sensitive attributes (optional). Activation requires an encryption certificate from the SP side. |
| Signature certificate / Signed request | This setting verifies SAML requests received from the Service Provider (SP) using the uploaded signing certificate. Enable this setting when using signed requests initiated by the SP. |
| Enable single logout / Single logout URL | Enable SLO (explained below) and specify the destination for the sign-out response. This can be configured after uploading the signing certificate. |
| Authentication context class | This is the requirement category for "which authentication method was used" to include in the assertion. It should match the SP (Service Provider) specification if one is provided. |
| Compliant with mandatory authentication | This setting determines whether to respect and request re-authentication when the Service Provider (SP) issues a ForceAuthn (re-authentication request every time). |
Attribute statement
User attribute and group information passed to the SP is defined in the "attribute statement".
However, attribute statements cannot be set during the App Integration Wizard (AIW). As shown in the diagram below, they are added and edited from the "Sign On" tab after app creation (Okta Expression Language is used to specify values).
→ Okta documentation: Configuring custom claims for app integrations
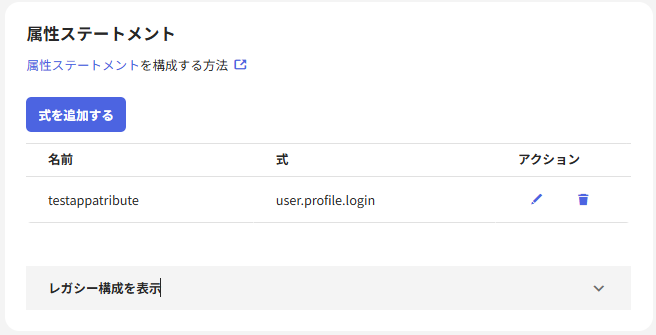
Figure: Attribute statement settings
Things to decide before implementation
- Check whether your company uses OIE or Classic Engine.
Okta's management interface and configuration options differ between the Identity Engine (OIE) and the Classic Engine. Please refer to the documentation appropriate for your environment (for OIE or Classic) for instructions. - Secure an emergency access method (backdoor).
If Okta, our Identity Provider (IdP), experiences an outage, administrators may be unable to access the application. Therefore, we will prepare emergency alternatives, such as local authentication other than SAML.
4. Advanced topics and more in-depth terminology
From here on, we will cover the more rigorous mechanisms, terminology, and Okta-specific advanced features that were omitted in Chapter 1.
"SAML Response" and "Assertion" are different things.
They are often confused, but the relationship between the two is like "envelope and its contents." The SP's ACS URL receives the outer Response, and the assertion is extracted from within that and verified.
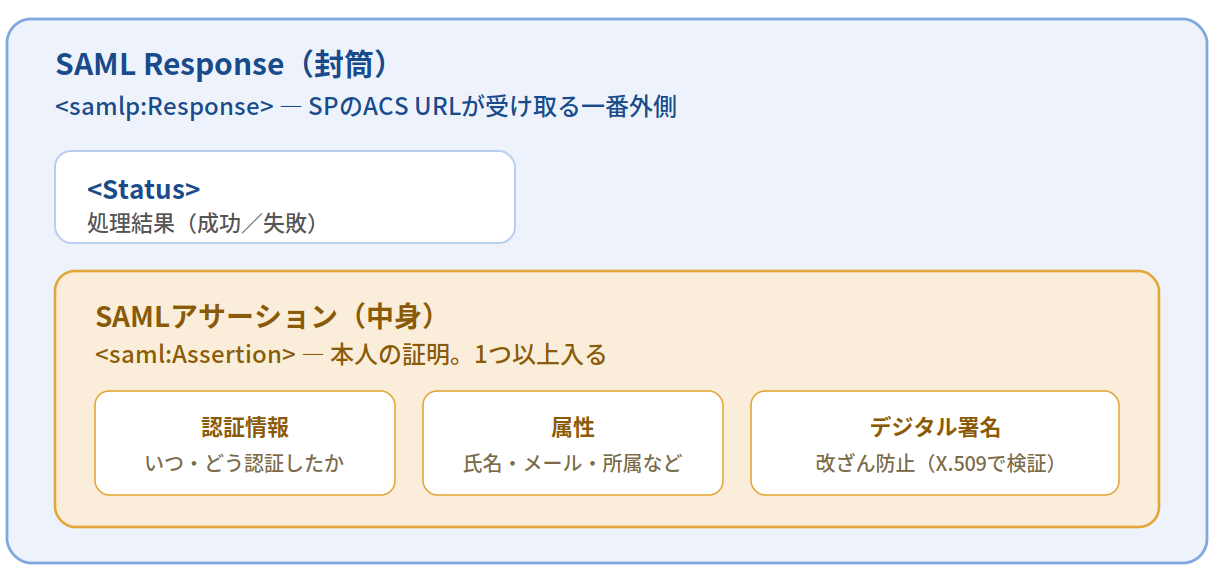
Figure: Nested structure of SAML Response and Assertion
[SAML 2.0 consists of four components]
The SAML specification consists of four layers with different roles. It is a structure that builds from foundational assertions to specific use cases (profiles).
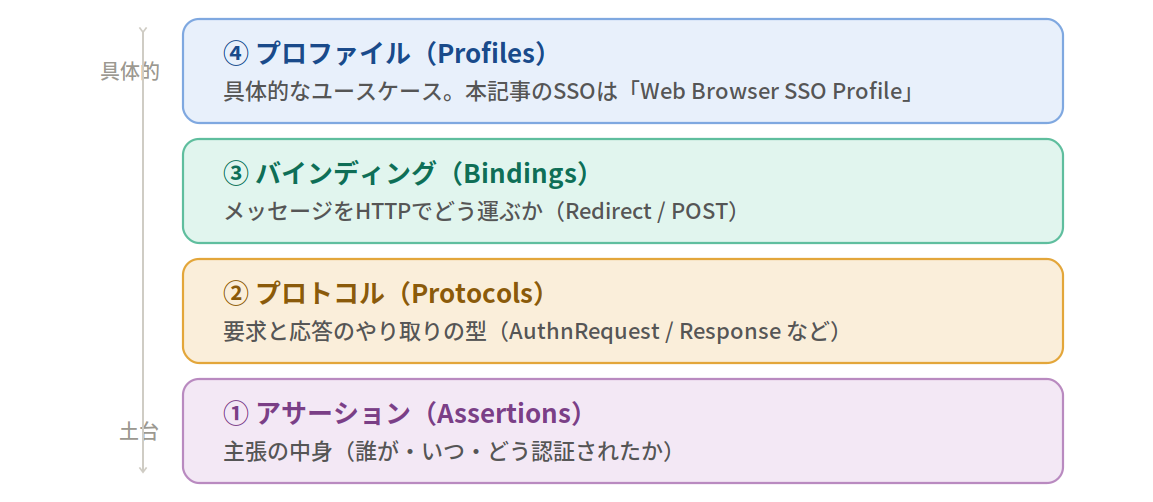
Figure: SAML 2.0 4-layer structure
Assertion-related elements that can be configured and checked in Okta
The following are items that can be configured and output controlled by Okta's AIW and features (general elements of the SAML specification are omitted).
| the term | Overview |
| Subject/Name ID | This is the part of the assertion that indicates "who" it is about. The <saml:NameID> within <saml:Subject> is the SP's identification key. The Format attribute specifies the type, and Okta's default is Unspecified. |
| Authentication context | This information indicates "how" the user was authenticated. It is represented by <AuthnContextClassRef>, and the Service Provider (SP) can determine whether or not MFA (Multi-Factor Authentication) was used. In Okta, this information can also be conveyed through the session.amr attribute (pwd, mfa, etc.). |
| Metadata | An XML document containing SP/IdP configuration information. It includes the Entity ID, each endpoint, and the X.509 certificate for signing. Exchanging this document automates trust configuration, and Okta provides the metadata URL. |
| Signatures and encryption | Signatures (XMLDSig) protect authenticity and integrity (genuine and tamper-proof) and are essential in SAML. Encryption (XML Encryption) protects confidentiality (hides the contents) and is optional in Okta. |
Single Logout (SLO): Single Logout
This feature allows users to terminate both their Okta session and their SP session in a single action when they press the SP logout button. This prevents situations where "the user logs out of the app, but Okta remains active."
[Okta's support status and limitations]
Okta's SLO only supports SP-initiated triggers. The Okta session ends when the SP sends a signed SLO request to Okta.
Furthermore, the Identity Engine (OIE) has a "Front-channel SLO (Multiple Device SLO)" feature, where Okta, upon receiving an SLO request initiated by the Service Provider (SP), sends a chain reaction of sign-out requests to other participating applications (a two-tiered structure: the initial trigger is initiated by the SP, and the notification from Okta to other applications is initiated by the Identity Provider (IdP)).
Furthermore, only some apps support SLOs. SWA apps do not support them, and SAML apps only support them if the SP can send signed SLO requests (please check the guide for each app to see if it supports them).
→ Okta documentation: Configuring single logout in app integration
→ Okta documentation: Configure Single Logout
Handling incompatible apps based on the IdP (Okta's proprietary method)
Even apps that only support SP-initiated flows can simulate IdP-initiated flows using Okta's Bookmark App integration (an icon is displayed on the dashboard and launched from there).
→ Okta documentation: Simulate IdP-initiated flows with the Bookmark app
Combination with MFA
Okta allows you to require MFA (Multi-Factor Authentication) before issuing an assertion. The assertion will include a statement indicating whether MFA has been used, and the Service Provider (SP) can verify this. It is also possible to explicitly pass the authentication method using the aforementioned session.amr attribute.
→ Okta documentation: SAML app integration
SAML vs. Other Protocols Comparison
| protocol | Main use | data form | Suitable scenarios |
| SAML 2.0 | SSO for businesses | XML | Integration with large corporations and existing systems, and high security requirements. |
| OIDC | Modern SSO and User Authentication | JSON / JWT | Mobile apps, SPAs, API-first design |
| OAuth 2.0 | API authorization | JSON / JWT | Delegation of access permissions to third-party APIs |
| SWA (Secure Web Authentication - Okta's proprietary technology) | SSO to unsupported apps | POST Form | Legacy apps that do not support SAML, OIDC, or WS-Federation. |
| WS-Federation | SSO for Microsoft products | XML | Older Microsoft products such as SharePoint |
5. Comparison and Selection Guide for SAML and OIDC
As a modern option, OIDC (OpenID Connect) is widely used alongside SAML. Okta recommends OIDC for new SSO integrations, and the choice between the two depends on the requirements.
[What is OIDC?]
OpenID Connect (OIDC) is an authentication standard that extends OAuth 2.0. While OAuth 2.0 handles authorization (delegation of access rights) to APIs, OIDC adds user authentication and SSO on top of that. It is a modern protocol that came later than SAML and has become widespread through large-scale adoption by Google and Microsoft. It uses lightweight tokens (ID tokens) in JSON format as certificates.
Detailed comparison table
Both SAML and OIDC enable identity federation, but their design philosophies are fundamentally different. The main differences are summarized in the table below.
| Comparison axis | SAML 2.0 | OIDC |
| data form | XML (signed) | JWT(JSON Web Token) |
| Year of formulation | 2005 (for enterprise use) | 2014 (for mobile and APIs) |
| Payload size | Large (several KB or more) | Lightweight (several hundred bytes or less) |
| Communication method | Browser redirect (POST / Redirect Binding) | Redirection + REST API (with backchannel communication) |
| Setting method | Manual exchange of metadata XML / static configuration | Dynamic automatic retrieval via discovery URL |
| Mobile Compatible | △ (Limited due to browser dependency) | ◎ (Also compatible with native apps and SPAs) |
| API authorization | △ (Not good at API protection) | ◎ (Directly protect the API with an access token) |
| Implementation difficulty | High (complex XML processing and signature verification) | Low to medium (Abundant SDKs) |
| Enterprise recruitment track record | ◎ (Strongly rooted in legacy systems and large corporations) | ○ (Standard in cloud-native companies) |
| Single Logout (SLO) | ◎ (Includes mature specifications) | ○ (Some vendors have specifications but are not making progress with implementation.) |
| Okta Recommendation | If there are requirements for integration with existing systems | Recommended for new integrations |
Comparison of JWT and SAML Assertion
Both OIDC ID tokens (JWT) and SAML assertions (XML) are "signed tokens that prove the user's identity," but their formats differ significantly. The main differences are as follows:
| perspective | SAML Assertion (Analyze) | JWT (ID Token) |
| format | XML tag structure | Base64 dot-separated string |
| size | Several KB or more (heavy) | Hundreds of bytes ~ (light) |
| Main use | SSO via browser | Mobile API SPA |
A major advantage of JWTs is their compact size, which allows them to be directly attached to the Authorization header of mobile apps and APIs.
Which should you choose: Selection framework
[Okta's official statement]
Okta recommends OIDC for new SSO integrations. OIDC is also recommended for apps newly registered with OIN (Okta Integration Network). SAML is positioned as an option to use for integration with existing systems or when there are specific requirements.
→ Source (Okta documentation): Overview of Single Sign-On in the OIN / Create an app integration
| In this situation | Recommended Protocol | cause |
| Building SSO integration for a new web application. | OIDC | It's easy to implement and has a rich SDK. Okta recommends it. |
| Implement SSO in mobile apps (iOS / Android) | OIDC | SAML is browser-dependent, making it unsuitable for native apps. |
| I want to protect my REST API with tokens. | OIDC + OAuth 2.0 | Access tokens can directly protect APIs. SAML is an indirect approach. |
| Integrate with existing SAML-enabled enterprise applications | SAML | If the other party's system only supports SAML, then SAML is the only option. |
| B2B collaboration with large corporations and government agencies | SAML | This is because SAML is often the standard in enterprise IdPs. |
| Strict SLOs are required. | SAML | The SAML SLO specification is mature and its implementation is stable. |
| Frontend SSO for SPA (React/Vue, etc.) | OIDC | You can securely obtain tokens using the Authorization Code + PKCE flow (the legacy Implicit flow is deprecated). |
The option of coexistence
SAML and OIDC are not mutually exclusive. In practice, large corporations often use them interchangeably depending on the purpose.
- Legacy apps → SAML, New apps → OIDC
Okta supports both as an IdP. You can maintain existing SAML integrations while adopting OIDC for new apps. - Okta absorbs protocol differences.
By using Okta as a hub, it's possible to configure the application to communicate solely via OIDC, while Okta handles communication with external SAML IdPs in the background.
[OIDC is not a "backward compatible" version of SAML.]
While OIDC is modern and easy to use, SAML has an advantage in areas where it excels (enterprise identity federation, attribute-based access control, and mature SLOs). It's not a case of "OIDC is better because it's newer," but rather a choice based on the use case.
6. Summary
SAML may seem complex, but its essence is simple: "A trusted IdP guarantees the identity of the individual, and the SP verifies that assertion."
- SP and IdP do not communicate directly.
The browser acts as an intermediary. The security of SAML is underpinned by this design. - Certificates (assertions) are protected by signatures.
The Identity Provider (IdP) digitally signs the assertion to prevent tampering and forgery. User attributes (such as group affiliations and roles) are included in the assertion. - There are two types of flows: SP-initiated and IdP-initiated.
Most cases originate from the Service Provider (SP). Cases originating from the Identity Provider (IdP) carry risks such as CSRF (Critical Share Fraud), so countermeasures are necessary during implementation. - Okta can be both an IdP and a SP.
It offers flexible implementation options that allow it to coexist with existing ID infrastructure. - For new connections, use OIDC; for enterprise integration, use SAML.
The choice isn't based on whether it's "modern or not," but rather on the target system, device, and implementation capabilities. Both can coexist via Okta.
Inquiry/Document request
In charge of Macnica Okta Co., Ltd.
- TEL:045-476-2010
- E-mail:okta@macnica.co.jp
Weekdays: 9:00-17:00