

Frontier
AI era
Security Frontline
The increasing use of AI within companies necessitates greater governance control.
Especially now, when things are changing so rapidly thanks to AI,
It is important to "correctly understand the necessary measures and take appropriate action."
The evolution of frontier AI is accelerating cyberattacks.
The increasing use of AI within companies necessitates greater governance control.
Especially now, when things are changing so rapidly thanks to AI,
"Understand the necessary measures correctly and take appropriate action."
This is important.
Changes in Threat Trends
AI will accelerate cyberattacks.
The evolution of frontier AI allows attackers to discover vulnerabilities, explore entry points, and take post-intrusion actions much faster.
Challenges faced by companies
Attacks are evolving with Frontier AI.
But I don't know where to start when it comes to strengthening security.
I don't know where to start.
The scope of what needs to be managed is expanding more than ever before.
Rapid patch application is not possible.
Applying the patch inevitably takes time.
We are likely to overlook important incidents.
A large number of alerts can lead to delays in making decisions about what is important.
I don't know the security situation.
There are many things that need to be managed, but it is difficult to grasp the current situation.
Flow of attack
Four steps in a cyberattack
An attack isn't a case of "it's over once they've infiltrated."
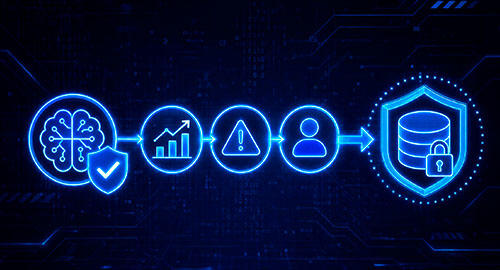
Since the attack progresses through multiple steps even after intrusion, stopping it at any point can prevent the attack from succeeding.
Specific examples of countermeasures
Organize the necessary countermeasures for your company according to each phase of the attack.
There isn't just one point where you can stop the attack.
The important thing is to "clarify which phases should be prioritized for countermeasures within your own company's environment."
identification
Preventive security
- CNAPP Cloud Protection
- SSPM SaaS Configuration Management
- ISPM ID configuration management
- IASM Internal Asset Management
- EASM External Asset Management
defense
Least privilege access control
- IDaaS Authentication Platform
- SASE Secure Access
- E-Browser: A browser for businesses.
- MSEG Network Isolation
- UEM terminal management
Detection and response
Advanced detection and attack response
- EDR Terminal Defense
- NDR Network Defense
- ITDR ID Defense
- ESP email defense
- SIEM Log Integration Analysis
- AI-SOC Operation Efficiency Improvement/Automation
restoration
Data recovery and encryption
- Cloud storage
- Data encryption
- backup
Key points for countermeasures
We will consider countermeasures from three perspectives.
Content
Changes in attacks in the Frontier AI era
Why not start by understanding the measures your company needs?
Watch the video to learn about the approach to countermeasures.
Check the documents
Free consultation